

-
Posts
511 -
Joined
-
Last visited
-
Days Won
36 -
Donations
0.01 USD

I develop stuff
Discord Level 19
Steam Accounts 2
Wizards 4
Achievements 8
Content Type
Profiles
Forums
News
Downloads
Everything posted by - Alex -
-
Moderation & Rule Enforcement Standard Organization-Wide Moderation Framework Public GGU moderation documentation — subject to revision as rules and server procedures change. Public Enforcement Standard: GGU publishes its moderation framework so players can understand how enforcement is expected to work. Specific evidence, private reports, personnel notes, and security-sensitive records may remain restricted. This standard defines organization-wide moderation principles used across GGU game servers, the Forums, Discord, TeamSpeak, and other community platforms. Game-specific procedures define the exact rule-to-punishment mappings unique to each game or server. Purpose Create consistent moderation expectations across GGU. Define who may take which types of action. Standardize evidence and documentation. Provide a predictable review and escalation path. Allow reasonable discretion without making enforcement arbitrary. Leadership & Review Structure Current GGU ranks and role holders are maintained at https://gguclan.com/ranks-and-roster/. Moderator — routine enforcement and temporary action within the applicable procedure. Staff — review Moderator actions, process bans, handle escalated moderation, and provide coaching. Manager — oversees the Game Team, serious disputes, exceptions, abuse reports, and final team-level decisions. Senior Manager — reviews unresolved Manager-level escalations and broader cross-team concerns. Operations Leader — handles organization-wide operational escalations and oversight of Senior Managers. Community Leader / Owner — reserved for major organization-wide disputes, serious leadership allegations, policy matters, or issues beyond delegated authority. Core Enforcement Principles Stop the violation. Protect players, services, and the community. Use the least severe action that reasonably addresses the situation. Apply similar rules consistently while still considering context. Preserve evidence for review. Escalate when authority, evidence, or impartiality is insufficient. Keep enforcement professional and avoid public arguments. Definitions Warning — formal or informal notice that behavior violates a rule. Mute / Gag / Silence — communication restriction according to platform capability. Kick — immediate removal from a server without an ongoing ban. Temporary Ban — time-limited removal pending expiration or review. Permanent Ban — indefinite removal subject to the applicable review or appeal process. Evasion — attempting to avoid an active punishment using alternate accounts, identities, connections, or methods. Evidence — screenshots, video/demos, logs, IDs, platform records, or other reliable records showing relevant conduct. Evidence Standard Capture enough context to understand what happened. Use evidence appropriate to the rule and platform. Preserve player/account identifiers where needed. Do not fabricate, selectively edit, or misleadingly crop evidence. Keep sensitive evidence private when public sharing would expose personal or security-sensitive information. More evidence is not automatically better; collect what is reasonably necessary. Moderator Temporary Ban Workflow Unless a current Game Team procedure explicitly states otherwise, Moderator-issued bans should be temporary and reviewed by Staff or higher Leadership. Confirm the player identity. Confirm the applicable rule. Collect the required evidence. Issue the temporary ban according to current Game Team procedure. Notify Staff or use the designated ban-review workflow. Staff reviews identity, evidence, rule, history where applicable, and final duration. Discretion Enforcement procedures are intended to create consistency, not eliminate judgment. A reasonable deviation may be appropriate when severity, intent, scale, technical limitations, history, or immediate risk materially changes the situation. Discretion Standard: A meaningful deviation from the normal progression should be explainable, proportionate, and reviewable. Discretion is not permission to ignore procedure because a Moderator dislikes or favors someone. Emergency Enforcement Immediate temporary action outside the normal progression may be used to stop active cheating, exploitation, malicious links, severe harassment, doxxing, DDoS threats, security risk, ban evasion, or large-scale disruption. Repeat Offenses Game-specific procedures should state when repeated violations increase punishment. Prior history should only affect the decision when the applicable procedure allows it. Punishment Evasion Attempts to evade an active punishment may justify additional enforcement. Preserve evidence linking the identities where practical. Cross-Game-Team Authority Authority in one Game Team does not automatically grant authority in another. Urgent concerns should be reported to the affected Game Team or higher GGU Leadership. Conflicts of Interest Moderators and Leaders should not control the review of their own disputed conduct when an independent reviewer is available. Personal disputes, close relationships, or direct involvement may require recusal. Appeals & Corrections Appeals should be reviewed by someone with appropriate authority. The original Moderator may provide evidence and context. Do not argue publicly over appeals. Correct demonstrably wrong actions without treating correction as a personal attack. A reasonable mistake is not automatically misconduct; repeated disregard, dishonesty, or abuse is more serious. Documentation Moderation records should allow another authorized reviewer to determine who acted, what rule applied, what evidence existed, and what action was taken. Prohibited Moderator Conduct Using moderation powers for personal disputes. Targeting disliked players or protecting friends. Falsifying evidence. Publicly arguing with players after an action. Mass punishment where individual enforcement is practical. Using administrative commands for harassment or disruption. Concealing mistakes or deleting evidence to avoid review. Consistent process first; game-specific penalties second.
-
AI-Assisted Development & Content Policy Review, Privacy & Responsibility This guide may be updated as GGU policies, procedures, platforms, and organizational needs change. Public Transparency: This policy is intentionally published for community transparency. The policy itself is public; credentials, recovery material, private personnel records, security-sensitive evidence, and other protected operational details remain restricted. Allowed Use AI tools may be used to assist with code, documentation, analysis, design ideation, and content when appropriate. Responsibility The human contributor remains responsible for correctness, security, licensing, and suitability. Sensitive Data Do not submit secrets, private credentials, confidential personnel information, or restricted data to unapproved external AI services. Code Review AI-generated code must receive the same testing and review expected of human-written code. Disclosure Document material AI use where required by a project, license, customer, or legal obligation. Scope This policy applies to GGU members, Leadership, contributors, partners, or systems to the extent they participate in or affect the activity described by this policy. Responsibilities Individuals are responsible for complying with the policy within their assigned access and duties. Managers are responsible for communicating expectations and correcting known violations within their area. Higher Leadership may interpret organization-wide questions, approve exceptions, or impose additional controls where risk requires it. Exceptions Exceptions should be limited, justified by a legitimate operational need, approved by the appropriate authority, and documented when they materially increase risk or depart from normal practice. Violations Violations may result in corrective instruction, removal of access, warning, suspension, demotion, removal from Leadership, removal from the community, or other action appropriate to the severity and circumstances. Review & Maintenance This policy should be reviewed when relevant systems, laws, platforms, organizational structure, or operational practices materially change. Verification Review factual claims. Review generated code for security issues. Run normal tests. Check licensing/provenance where relevant. Do not rely on generated output as authority for policy or legal conclusions. Sensitive Inputs Never paste production credentials, private keys, access tokens, confidential personnel records, or unreleased security details into unapproved external AI tools. Definitions & Interpretation Where a term is not specifically defined in this policy, it should be interpreted using its ordinary GGU operational meaning and related published guides. When two policies appear to conflict, the more specific policy should generally control for its subject matter unless higher Leadership directs otherwise. Policy Ownership Each policy should have an identifiable organizational owner responsible for periodic review, proposed updates, and resolving routine interpretation questions. Ownership of the policy does not grant unlimited authority to waive it. Records & Evidence Keep records that are reasonably necessary to demonstrate approvals, access changes, disciplinary actions, incidents, or exceptions. Store sensitive records in appropriately restricted locations. Do not create unnecessary collections of personal information. Do not alter or delete records to conceal mistakes or avoid review. Where an action is logged automatically, preserve the relevant log rather than duplicating it manually without need. Good-Faith Reporting Members and Leaders should be able to report suspected policy violations in good faith without retaliation. Knowingly false reports, fabricated evidence, or malicious misuse of reporting processes may themselves be addressed as misconduct. Policy Changes Material policy changes should be communicated to affected people. Changes that alter access, enforcement, or Leadership obligations should include enough explanation for people to understand what changed and when the new expectation applies. High-Risk Uses Security-sensitive code Authentication/authorization Production database migrations Legal/policy conclusions Public claims presented as factual Automated moderation or personnel decisions These uses require stronger human review and should not rely on AI output as the sole basis for the decision. Policy protects the community when expectations are clear before problems happen.
-
Source Code & Intellectual Property Policy Ownership, Licensing & Project Stewardship Public GGU policy — subject to revision as systems, responsibilities, and operational practices change. Public Transparency: This policy is intentionally published so the community can understand GGU's standards and accountability. Credentials, recovery material, private personnel records, and active security-sensitive details remain restricted. This policy defines how GGU-developed source code, configuration, documentation, designs, and related technical work should be owned, licensed, stored, reused, and maintained. Purpose Source-control workflow and intellectual-property ownership are separate concerns. This policy exists so ownership, licensing, and stewardship are handled explicitly rather than being buried inside repository-usage rules. Scope This policy applies to source code, scripts, configuration, templates, documentation, build systems, automation, infrastructure definitions, graphics, technical assets, and other work created for GGU projects. Project Stewardship Operational projects should live in approved GGU-controlled repositories or other approved shared storage. Projects should identify maintainers or responsible Teams. Deployment and recovery information should not exist only on one person's computer. Repositories should contain enough documentation for another authorized maintainer to understand the project. Ownership Must Be Explicit GGU should not rely on vague assumptions about ownership. Projects with special contributor, licensing, commissioned-work, partnership, or external ownership arrangements should document those terms explicitly. Work Created for GGU Where a contributor creates work specifically as part of an assigned GGU role or approved GGU project, the intended ownership or license should be defined by the project or contributor arrangement. If no special terms exist, Leadership should resolve ownership before publication, commercial use, relicensing, or transfer. Existing Personal Projects A contributor may bring pre-existing code, assets, or tools into a GGU project only when they have the right to do so. Pre-existing ownership should be identified rather than silently treated as newly created GGU work. Third-Party Code & Assets Respect software and asset licenses. Preserve attribution and notices where required. Do not copy proprietary source or assets without permission. Do not use dependencies whose licensing conflicts with the intended project distribution without review. Track important third-party dependencies where practical. Open Source Before publishing a GGU project as open source, verify that it contains no secrets, private member data, restricted infrastructure details, or third-party material that cannot legally be redistributed. The chosen license should be deliberate. Closed Source Closed-source GGU repositories remain restricted to authorized users. Private status does not eliminate the need to define contributor rights, third-party licensing obligations, or project ownership. Contributor Rights & Credit GGU should reasonably preserve contributor credit where appropriate. Credit does not automatically grant ongoing administrative access, ownership of unrelated project components, or a right to prevent operational maintenance after the contributor leaves. Departure or Role Change Operational source and documentation must remain accessible to GGU. Departing contributors should transfer project knowledge and ownership of deployment processes. Personal credentials should be removed or replaced. Shared secrets known to departing users should be rotated when appropriate. A departing contributor must not intentionally withhold required operational code, configuration, or documentation. Forking & Reuse Reuse of GGU code or assets outside GGU depends on the applicable license, ownership, project agreement, or explicit approval. Public availability alone does not automatically grant unrestricted reuse unless the published license permits it. AI-Assisted Contributions AI-assisted code or content is still subject to the same ownership, licensing, security, review, and third-party provenance requirements as human-created work. Disputes Ownership or licensing disputes should be escalated to Community Leadership or the Owner before code is published, relicensed, sold, transferred, or removed from GGU control. Documentation Projects with non-standard ownership or licensing terms should document those terms in an appropriate repository or organizational record. Related Policy Git / Gitea Repository Usage Policy AI-Assisted Development & Content Policy Third-Party & Partner Access Policy Make ownership explicit before it becomes a dispute.
-
Third-Party & Partner Access Policy External Access, Approval & Expiration This guide may be updated as GGU policies, procedures, platforms, and organizational needs change. Public Transparency: This policy is intentionally published for community transparency. The policy itself is public; credentials, recovery material, private personnel records, security-sensitive evidence, and other protected operational details remain restricted. Approval External access requires an internal GGU owner and explicit approval. Scope Grant the minimum access required for the partnership or task. Expiration Temporary partner access should have an expected review or end point. Confidentiality Partners must not receive internal or sensitive information beyond what is required. Offboarding Remove access when the relationship or task ends. Scope This policy applies to GGU members, Leadership, contributors, partners, or systems to the extent they participate in or affect the activity described by this policy. Responsibilities Individuals are responsible for complying with the policy within their assigned access and duties. Managers are responsible for communicating expectations and correcting known violations within their area. Higher Leadership may interpret organization-wide questions, approve exceptions, or impose additional controls where risk requires it. Exceptions Exceptions should be limited, justified by a legitimate operational need, approved by the appropriate authority, and documented when they materially increase risk or depart from normal practice. Violations Violations may result in corrective instruction, removal of access, warning, suspension, demotion, removal from Leadership, removal from the community, or other action appropriate to the severity and circumstances. Review & Maintenance This policy should be reviewed when relevant systems, laws, platforms, organizational structure, or operational practices materially change. Internal Sponsor Every external account or partner access grant should have an internal GGU owner responsible for scope, review, and removal. Review Triggers Project completion. Contract/relationship change. Long inactivity. Security incident. Role change of internal sponsor. Expansion of requested permissions. Definitions & Interpretation Where a term is not specifically defined in this policy, it should be interpreted using its ordinary GGU operational meaning and related published guides. When two policies appear to conflict, the more specific policy should generally control for its subject matter unless higher Leadership directs otherwise. Policy Ownership Each policy should have an identifiable organizational owner responsible for periodic review, proposed updates, and resolving routine interpretation questions. Ownership of the policy does not grant unlimited authority to waive it. Records & Evidence Keep records that are reasonably necessary to demonstrate approvals, access changes, disciplinary actions, incidents, or exceptions. Store sensitive records in appropriately restricted locations. Do not create unnecessary collections of personal information. Do not alter or delete records to conceal mistakes or avoid review. Where an action is logged automatically, preserve the relevant log rather than duplicating it manually without need. Good-Faith Reporting Members and Leaders should be able to report suspected policy violations in good faith without retaliation. Knowingly false reports, fabricated evidence, or malicious misuse of reporting processes may themselves be addressed as misconduct. Policy Changes Material policy changes should be communicated to affected people. Changes that alter access, enforcement, or Leadership obligations should include enough explanation for people to understand what changed and when the new expectation applies. Policy protects the community when expectations are clear before problems happen.
-
Incident Response & Security Reporting Policy Security, Outages & Evidence Preservation This guide may be updated as GGU policies, procedures, platforms, and organizational needs change. Public Transparency: This policy is intentionally published for community transparency. The policy itself is public; credentials, recovery material, private personnel records, security-sensitive evidence, and other protected operational details remain restricted. Report Immediately Compromised accounts Exposed credentials Unauthorized access Data loss Major outages Malicious administrative changes Serious vulnerabilities Preservation Preserve logs and evidence. Do not delete or alter records to conceal mistakes. Containment Restrict access or isolate systems when necessary to stop active harm. Post-Incident Significant incidents should receive a documented review and follow-up actions. Scope This policy applies to GGU members, Leadership, contributors, partners, or systems to the extent they participate in or affect the activity described by this policy. Responsibilities Individuals are responsible for complying with the policy within their assigned access and duties. Managers are responsible for communicating expectations and correcting known violations within their area. Higher Leadership may interpret organization-wide questions, approve exceptions, or impose additional controls where risk requires it. Exceptions Exceptions should be limited, justified by a legitimate operational need, approved by the appropriate authority, and documented when they materially increase risk or depart from normal practice. Violations Violations may result in corrective instruction, removal of access, warning, suspension, demotion, removal from Leadership, removal from the community, or other action appropriate to the severity and circumstances. Review & Maintenance This policy should be reviewed when relevant systems, laws, platforms, organizational structure, or operational practices materially change. Reporting Channel Security-sensitive incidents should be reported through a restricted Leadership or technical channel rather than public Discord channels. Do Not Conceal Mistakes must be reported promptly. Concealing an incident, deleting logs, or falsifying the timeline is itself a serious policy violation. Definitions & Interpretation Where a term is not specifically defined in this policy, it should be interpreted using its ordinary GGU operational meaning and related published guides. When two policies appear to conflict, the more specific policy should generally control for its subject matter unless higher Leadership directs otherwise. Policy Ownership Each policy should have an identifiable organizational owner responsible for periodic review, proposed updates, and resolving routine interpretation questions. Ownership of the policy does not grant unlimited authority to waive it. Records & Evidence Keep records that are reasonably necessary to demonstrate approvals, access changes, disciplinary actions, incidents, or exceptions. Store sensitive records in appropriately restricted locations. Do not create unnecessary collections of personal information. Do not alter or delete records to conceal mistakes or avoid review. Where an action is logged automatically, preserve the relevant log rather than duplicating it manually without need. Good-Faith Reporting Members and Leaders should be able to report suspected policy violations in good faith without retaliation. Knowingly false reports, fabricated evidence, or malicious misuse of reporting processes may themselves be addressed as misconduct. Policy Changes Material policy changes should be communicated to affected people. Changes that alter access, enforcement, or Leadership obligations should include enough explanation for people to understand what changed and when the new expectation applies. Severity & Notification Incidents with broad service impact, administrative compromise, exposed secrets, or suspected unauthorized access should be escalated quickly to technical and organizational Leadership. Routine single-service errors can remain within the responsible Team unless the impact expands. Policy protects the community when expectations are clear before problems happen.
-
Conflict of Interest & Recusal Policy Impartial Leadership Decisions This guide may be updated as GGU policies, procedures, platforms, and organizational needs change. Public Transparency: This policy is intentionally published for community transparency. The policy itself is public; credentials, recovery material, private personnel records, security-sensitive evidence, and other protected operational details remain restricted. Conflict A conflict exists when personal relationships, disputes, financial interests, or direct involvement could reasonably affect impartial judgment. Recusal Leaders should recuse from abuse reports, personnel decisions, appeals, or investigations where they cannot reasonably be impartial. Escalation Route the matter to the next appropriate Leader. Scope This policy applies to GGU members, Leadership, contributors, partners, or systems to the extent they participate in or affect the activity described by this policy. Responsibilities Individuals are responsible for complying with the policy within their assigned access and duties. Managers are responsible for communicating expectations and correcting known violations within their area. Higher Leadership may interpret organization-wide questions, approve exceptions, or impose additional controls where risk requires it. Exceptions Exceptions should be limited, justified by a legitimate operational need, approved by the appropriate authority, and documented when they materially increase risk or depart from normal practice. Violations Violations may result in corrective instruction, removal of access, warning, suspension, demotion, removal from Leadership, removal from the community, or other action appropriate to the severity and circumstances. Review & Maintenance This policy should be reviewed when relevant systems, laws, platforms, organizational structure, or operational practices materially change. Examples of Conflict Close personal relationship with a subject of review. Active personal dispute. Direct involvement in the incident. Financial or project interest in the outcome. Prior public commitment to a particular result. Recusal Does Not Mean Silence A recused Leader may still provide relevant factual evidence, but should not control the outcome. Definitions & Interpretation Where a term is not specifically defined in this policy, it should be interpreted using its ordinary GGU operational meaning and related published guides. When two policies appear to conflict, the more specific policy should generally control for its subject matter unless higher Leadership directs otherwise. Policy Ownership Each policy should have an identifiable organizational owner responsible for periodic review, proposed updates, and resolving routine interpretation questions. Ownership of the policy does not grant unlimited authority to waive it. Records & Evidence Keep records that are reasonably necessary to demonstrate approvals, access changes, disciplinary actions, incidents, or exceptions. Store sensitive records in appropriately restricted locations. Do not create unnecessary collections of personal information. Do not alter or delete records to conceal mistakes or avoid review. Where an action is logged automatically, preserve the relevant log rather than duplicating it manually without need. Good-Faith Reporting Members and Leaders should be able to report suspected policy violations in good faith without retaliation. Knowingly false reports, fabricated evidence, or malicious misuse of reporting processes may themselves be addressed as misconduct. Policy Changes Material policy changes should be communicated to affected people. Changes that alter access, enforcement, or Leadership obligations should include enough explanation for people to understand what changed and when the new expectation applies. GGU Leadership Hierarchy The general organization-wide Leadership hierarchy is: Community Leader — highest community leadership layer and organization-wide oversight. Operations Leader — day-to-day organization-wide operations and direct oversight of Senior Managers. Senior Manager — oversees Managers and broader operational areas. Manager — directly manages an individual Team or Department. Staff — game-server Leadership supporting Managers and Moderators. Moderator — routine game-server moderation and enforcement. Escalation: For organization-wide escalation, the normal path is Moderator → Staff → Manager → Senior Manager → Operations Leader → Community Leader. Not every issue must pass through every level. Current Leadership Assignments Current role holders are maintained on the GGU Ranks & Roster page. This policy governs the role regardless of who currently holds it. Policy protects the community when expectations are clear before problems happen.
-
Leadership Promotion, Demotion & Discipline Policy Fair Personnel Decisions & Access Changes This guide may be updated as GGU policies, procedures, platforms, and organizational needs change. Public Transparency: This policy is intentionally published for community transparency. The policy itself is public; credentials, recovery material, private personnel records, security-sensitive evidence, and other protected operational details remain restricted. Promotions Promotions should reflect organizational need, demonstrated readiness, judgment, conduct, and ability to perform the role. Corrective Action Where appropriate, Leaders should identify the concern, provide expectations, offer reasonable support, and follow up. Immediate Action Serious misconduct, security risk, or abuse of access may justify immediate suspension or removal of permissions pending review. Demotions Remove only affected access and document the transition. Review Higher Leadership may review disputed personnel decisions. Scope This policy applies to GGU members, Leadership, contributors, partners, or systems to the extent they participate in or affect the activity described by this policy. Responsibilities Individuals are responsible for complying with the policy within their assigned access and duties. Managers are responsible for communicating expectations and correcting known violations within their area. Higher Leadership may interpret organization-wide questions, approve exceptions, or impose additional controls where risk requires it. Exceptions Exceptions should be limited, justified by a legitimate operational need, approved by the appropriate authority, and documented when they materially increase risk or depart from normal practice. Violations Violations may result in corrective instruction, removal of access, warning, suspension, demotion, removal from Leadership, removal from the community, or other action appropriate to the severity and circumstances. Review & Maintenance This policy should be reviewed when relevant systems, laws, platforms, organizational structure, or operational practices materially change. Progressive Discipline Progressive discipline is appropriate when improvement is realistic and immediate removal is not required. Serious abuse, security risk, dishonesty, harassment, or destructive conduct may justify skipping intermediate steps. Documentation Significant disciplinary decisions should include enough factual documentation to support later review without turning personnel records into subjective commentary. Definitions & Interpretation Where a term is not specifically defined in this policy, it should be interpreted using its ordinary GGU operational meaning and related published guides. When two policies appear to conflict, the more specific policy should generally control for its subject matter unless higher Leadership directs otherwise. Policy Ownership Each policy should have an identifiable organizational owner responsible for periodic review, proposed updates, and resolving routine interpretation questions. Ownership of the policy does not grant unlimited authority to waive it. Records & Evidence Keep records that are reasonably necessary to demonstrate approvals, access changes, disciplinary actions, incidents, or exceptions. Store sensitive records in appropriately restricted locations. Do not create unnecessary collections of personal information. Do not alter or delete records to conceal mistakes or avoid review. Where an action is logged automatically, preserve the relevant log rather than duplicating it manually without need. Good-Faith Reporting Members and Leaders should be able to report suspected policy violations in good faith without retaliation. Knowingly false reports, fabricated evidence, or malicious misuse of reporting processes may themselves be addressed as misconduct. Policy Changes Material policy changes should be communicated to affected people. Changes that alter access, enforcement, or Leadership obligations should include enough explanation for people to understand what changed and when the new expectation applies. Decision Factors Severity Intent Pattern/repetition Impact Prior coaching or warnings Honesty during review Ability to safely continue in the role Access During Review Temporary restriction of sensitive access is not necessarily a final disciplinary finding. It may be used to protect GGU while facts are being reviewed. GGU Leadership Hierarchy The general organization-wide Leadership hierarchy is: Community Leader — highest community leadership layer and organization-wide oversight. Operations Leader — day-to-day organization-wide operations and direct oversight of Senior Managers. Senior Manager — oversees Managers and broader operational areas. Manager — directly manages an individual Team or Department. Staff — game-server Leadership supporting Managers and Moderators. Moderator — routine game-server moderation and enforcement. Escalation: For organization-wide escalation, the normal path is Moderator → Staff → Manager → Senior Manager → Operations Leader → Community Leader. Not every issue must pass through every level. Operations Leader Authority The Operations Leader oversees Senior Managers and may participate in or approve Leadership personnel decisions within delegated authority. Matters involving the Operations Leader, Community Leaders, or major organization-wide restructuring should be reviewed by Community Leadership or as appropriate. Current Leadership Assignments Current role holders are maintained on the GGU Ranks & Roster page. This policy governs the role regardless of who currently holds it. Policy protects the community when expectations are clear before problems happen.
-
Leadership Leave, Inactivity & Resignation Policy Coverage, Notice & Role Continuity This guide may be updated as GGU policies, procedures, platforms, and organizational needs change. Public Transparency: This policy is intentionally published for community transparency. The policy itself is public; credentials, recovery material, private personnel records, security-sensitive evidence, and other protected operational details remain restricted. Leave Leaders expecting an extended absence should notify their direct Leader and arrange coverage for time-sensitive responsibilities. Inactivity Leadership positions require enough activity to perform assigned responsibilities. Expectations should be evaluated by role, not one universal metric. Resignation Reasonable notice is encouraged. Access and responsibilities must be handed off using the Leadership Offboarding Checklist. Retired Leadership Eligibility should be handled under the current Retired Leadership standard and may depend on service history and departure in good standing. Scope This policy applies to GGU members, Leadership, contributors, partners, or systems to the extent they participate in or affect the activity described by this policy. Responsibilities Individuals are responsible for complying with the policy within their assigned access and duties. Managers are responsible for communicating expectations and correcting known violations within their area. Higher Leadership may interpret organization-wide questions, approve exceptions, or impose additional controls where risk requires it. Exceptions Exceptions should be limited, justified by a legitimate operational need, approved by the appropriate authority, and documented when they materially increase risk or depart from normal practice. Violations Violations may result in corrective instruction, removal of access, warning, suspension, demotion, removal from Leadership, removal from the community, or other action appropriate to the severity and circumstances. Review & Maintenance This policy should be reviewed when relevant systems, laws, platforms, organizational structure, or operational practices materially change. Leadership Coverage Before extended leave, identify who owns urgent decisions, active projects, staff questions, and production access during the absence. Unresponsive Leadership When a Leader becomes unexpectedly unreachable, higher Leadership may temporarily reassign responsibilities and restrict sensitive access until status is clarified. Definitions & Interpretation Where a term is not specifically defined in this policy, it should be interpreted using its ordinary GGU operational meaning and related published guides. When two policies appear to conflict, the more specific policy should generally control for its subject matter unless higher Leadership directs otherwise. Policy Ownership Each policy should have an identifiable organizational owner responsible for periodic review, proposed updates, and resolving routine interpretation questions. Ownership of the policy does not grant unlimited authority to waive it. Records & Evidence Keep records that are reasonably necessary to demonstrate approvals, access changes, disciplinary actions, incidents, or exceptions. Store sensitive records in appropriately restricted locations. Do not create unnecessary collections of personal information. Do not alter or delete records to conceal mistakes or avoid review. Where an action is logged automatically, preserve the relevant log rather than duplicating it manually without need. Good-Faith Reporting Members and Leaders should be able to report suspected policy violations in good faith without retaliation. Knowingly false reports, fabricated evidence, or malicious misuse of reporting processes may themselves be addressed as misconduct. Policy Changes Material policy changes should be communicated to affected people. Changes that alter access, enforcement, or Leadership obligations should include enough explanation for people to understand what changed and when the new expectation applies. GGU Leadership Hierarchy The general organization-wide Leadership hierarchy is: Community Leader — highest community leadership layer and organization-wide oversight. Operations Leader — day-to-day organization-wide operations and direct oversight of Senior Managers. Senior Manager — oversees Managers and broader operational areas. Manager — directly manages an individual Team or Department. Staff — game-server Leadership supporting Managers and Moderators. Moderator — routine game-server moderation and enforcement. Escalation: For organization-wide escalation, the normal path is Moderator → Staff → Manager → Senior Manager → Operations Leader → Community Leader. Not every issue must pass through every level. Current Leadership Assignments Current role holders are maintained on the GGU Ranks & Roster page. This policy governs the role regardless of who currently holds it. Policy protects the community when expectations are clear before problems happen.
-
Member Activity & Leave of Absence Policy Community Participation & Extended Absence This guide may be updated as GGU policies, procedures, platforms, and organizational needs change. Public Transparency: This policy is intentionally published for community transparency. The policy itself is public; credentials, recovery material, private personnel records, security-sensitive evidence, and other protected operational details remain restricted. Activity Members are encouraged to remain reasonably involved through servers, Discord, Forums, events, guilds, or community projects. Extended Absence Members who expect an extended absence may use the current Leave of Absence process where applicable. No Fixed Purge in This Policy If GGU adopts a formal inactivity review cadence, it should be published explicitly rather than implied by outdated guides. Return Returning members should contact Leadership if roles or access require restoration. Scope This policy applies to GGU members, Leadership, contributors, partners, or systems to the extent they participate in or affect the activity described by this policy. Responsibilities Individuals are responsible for complying with the policy within their assigned access and duties. Managers are responsible for communicating expectations and correcting known violations within their area. Higher Leadership may interpret organization-wide questions, approve exceptions, or impose additional controls where risk requires it. Exceptions Exceptions should be limited, justified by a legitimate operational need, approved by the appropriate authority, and documented when they materially increase risk or depart from normal practice. Violations Violations may result in corrective instruction, removal of access, warning, suspension, demotion, removal from Leadership, removal from the community, or other action appropriate to the severity and circumstances. Review & Maintenance This policy should be reviewed when relevant systems, laws, platforms, organizational structure, or operational practices materially change. Activity Standard GGU should evaluate activity using meaningful participation rather than a single platform-presence metric. Server play, Discord, Forums, events, guilds, and project participation may all demonstrate involvement. Inactivity Reviews If GGU performs membership inactivity reviews, the current cadence and consequences should be published separately or in this policy before enforcement. Definitions & Interpretation Where a term is not specifically defined in this policy, it should be interpreted using its ordinary GGU operational meaning and related published guides. When two policies appear to conflict, the more specific policy should generally control for its subject matter unless higher Leadership directs otherwise. Policy Ownership Each policy should have an identifiable organizational owner responsible for periodic review, proposed updates, and resolving routine interpretation questions. Ownership of the policy does not grant unlimited authority to waive it. Records & Evidence Keep records that are reasonably necessary to demonstrate approvals, access changes, disciplinary actions, incidents, or exceptions. Store sensitive records in appropriately restricted locations. Do not create unnecessary collections of personal information. Do not alter or delete records to conceal mistakes or avoid review. Where an action is logged automatically, preserve the relevant log rather than duplicating it manually without need. Good-Faith Reporting Members and Leaders should be able to report suspected policy violations in good faith without retaliation. Knowingly false reports, fabricated evidence, or malicious misuse of reporting processes may themselves be addressed as misconduct. Policy Changes Material policy changes should be communicated to affected people. Changes that alter access, enforcement, or Leadership obligations should include enough explanation for people to understand what changed and when the new expectation applies. Policy protects the community when expectations are clear before problems happen.
-
Change Management & Production Access Policy Production Changes, Review & Rollback This guide may be updated as GGU policies, procedures, platforms, and organizational needs change. Public Transparency: This policy is intentionally published for community transparency. The policy itself is public; credentials, recovery material, private personnel records, security-sensitive evidence, and other protected operational details remain restricted. Purpose Production changes should be intentional, reviewable, and recoverable. Requirements Back up or ensure rollback capability for high-impact changes. Use testing/review before production when practical. Avoid unrelated changes during incidents. Document significant production changes. Restrict production access to people who require it. Emergency Changes Emergency changes may bypass normal review when delay would create greater risk, but must be documented afterward. Scope This policy applies to GGU members, Leadership, contributors, partners, or systems to the extent they participate in or affect the activity described by this policy. Responsibilities Individuals are responsible for complying with the policy within their assigned access and duties. Managers are responsible for communicating expectations and correcting known violations within their area. Higher Leadership may interpret organization-wide questions, approve exceptions, or impose additional controls where risk requires it. Exceptions Exceptions should be limited, justified by a legitimate operational need, approved by the appropriate authority, and documented when they materially increase risk or depart from normal practice. Violations Violations may result in corrective instruction, removal of access, warning, suspension, demotion, removal from Leadership, removal from the community, or other action appropriate to the severity and circumstances. Review & Maintenance This policy should be reviewed when relevant systems, laws, platforms, organizational structure, or operational practices materially change. Standard Change Define the change. Assess impact. Back up/prepare rollback. Review/test where appropriate. Deploy. Validate. Document. Emergency Change Emergency changes may move directly from assessment to deployment when delay is more dangerous than change risk. They still require validation and after-the-fact documentation. Definitions & Interpretation Where a term is not specifically defined in this policy, it should be interpreted using its ordinary GGU operational meaning and related published guides. When two policies appear to conflict, the more specific policy should generally control for its subject matter unless higher Leadership directs otherwise. Policy Ownership Each policy should have an identifiable organizational owner responsible for periodic review, proposed updates, and resolving routine interpretation questions. Ownership of the policy does not grant unlimited authority to waive it. Records & Evidence Keep records that are reasonably necessary to demonstrate approvals, access changes, disciplinary actions, incidents, or exceptions. Store sensitive records in appropriately restricted locations. Do not create unnecessary collections of personal information. Do not alter or delete records to conceal mistakes or avoid review. Where an action is logged automatically, preserve the relevant log rather than duplicating it manually without need. Good-Faith Reporting Members and Leaders should be able to report suspected policy violations in good faith without retaliation. Knowingly false reports, fabricated evidence, or malicious misuse of reporting processes may themselves be addressed as misconduct. Policy Changes Material policy changes should be communicated to affected people. Changes that alter access, enforcement, or Leadership obligations should include enough explanation for people to understand what changed and when the new expectation applies. Change Risk Low risk: reversible content/configuration change with limited impact. Moderate risk: service restart, plugin update, permission change, or multi-user impact. High risk: database migration, authentication change, network/firewall change, destructive storage operation, or organization-wide production deployment. Review and rollback expectations should increase with risk. Policy protects the community when expectations are clear before problems happen.
-
Data Classification & Confidentiality Policy Handling Public, Internal & Sensitive Information This guide may be updated as GGU policies, procedures, platforms, and organizational needs change. Public Transparency: This policy is intentionally published for community transparency. The policy itself is public; credentials, recovery material, private personnel records, security-sensitive evidence, and other protected operational details remain restricted. Public Information intended for community or public distribution. Internal Routine operational information intended for GGU Staff/Leadership. Leadership-Only Personnel discussions, abuse reports, internal investigations, non-public planning, and privileged moderation information. Security-Sensitive Passwords, tokens, private keys, vulnerability details, infrastructure secrets, recovery codes, and other data whose exposure creates direct risk. Handling Share information only with people who need it. Do not post sensitive screenshots/logs in public channels. Scope This policy applies to GGU members, Leadership, contributors, partners, or systems to the extent they participate in or affect the activity described by this policy. Responsibilities Individuals are responsible for complying with the policy within their assigned access and duties. Managers are responsible for communicating expectations and correcting known violations within their area. Higher Leadership may interpret organization-wide questions, approve exceptions, or impose additional controls where risk requires it. Exceptions Exceptions should be limited, justified by a legitimate operational need, approved by the appropriate authority, and documented when they materially increase risk or depart from normal practice. Violations Violations may result in corrective instruction, removal of access, warning, suspension, demotion, removal from Leadership, removal from the community, or other action appropriate to the severity and circumstances. Review & Maintenance This policy should be reviewed when relevant systems, laws, platforms, organizational structure, or operational practices materially change. Handling by Classification Public: may be shared openly. Internal: share within GGU where operationally useful. Leadership-Only: limit to authorized Leadership with a need to know. Security-Sensitive: use approved secure storage and avoid routine chat transmission. Retention Do not retain sensitive information longer than necessary simply because storage is available. Preserve records that are needed for moderation, security, legal, or operational continuity. Definitions & Interpretation Where a term is not specifically defined in this policy, it should be interpreted using its ordinary GGU operational meaning and related published guides. When two policies appear to conflict, the more specific policy should generally control for its subject matter unless higher Leadership directs otherwise. Policy Ownership Each policy should have an identifiable organizational owner responsible for periodic review, proposed updates, and resolving routine interpretation questions. Ownership of the policy does not grant unlimited authority to waive it. Records & Evidence Keep records that are reasonably necessary to demonstrate approvals, access changes, disciplinary actions, incidents, or exceptions. Store sensitive records in appropriately restricted locations. Do not create unnecessary collections of personal information. Do not alter or delete records to conceal mistakes or avoid review. Where an action is logged automatically, preserve the relevant log rather than duplicating it manually without need. Good-Faith Reporting Members and Leaders should be able to report suspected policy violations in good faith without retaliation. Knowingly false reports, fabricated evidence, or malicious misuse of reporting processes may themselves be addressed as misconduct. Policy Changes Material policy changes should be communicated to affected people. Changes that alter access, enforcement, or Leadership obligations should include enough explanation for people to understand what changed and when the new expectation applies. Examples Public: published rules, public announcements, server listings. Internal: routine project coordination, non-sensitive operational notes. Leadership-Only: staff performance discussions, abuse reports, private moderation evidence. Security-Sensitive: passwords, tokens, infrastructure recovery information, unreleased vulnerability details. Policy protects the community when expectations are clear before problems happen.
-
Administrative Access & Account Security Policy Credentials, 2FA & Least Privilege This guide may be updated as GGU policies, procedures, platforms, and organizational needs change. Public Transparency: This policy is intentionally published for community transparency. The policy itself is public; credentials, recovery material, private personnel records, security-sensitive evidence, and other protected operational details remain restricted. Requirements Use unique credentials. Enable two-factor authentication where supported. Do not share personal administrative accounts. Use least privilege. Report suspected compromise immediately. Remove obsolete access promptly. Shared Access Prefer service accounts, team-managed secrets, or delegated access over shared personal credentials. Access Reviews Managers and system owners should periodically review elevated access and after role changes. Scope This policy applies to GGU members, Leadership, contributors, partners, or systems to the extent they participate in or affect the activity described by this policy. Responsibilities Individuals are responsible for complying with the policy within their assigned access and duties. Managers are responsible for communicating expectations and correcting known violations within their area. Higher Leadership may interpret organization-wide questions, approve exceptions, or impose additional controls where risk requires it. Exceptions Exceptions should be limited, justified by a legitimate operational need, approved by the appropriate authority, and documented when they materially increase risk or depart from normal practice. Violations Violations may result in corrective instruction, removal of access, warning, suspension, demotion, removal from Leadership, removal from the community, or other action appropriate to the severity and circumstances. Review & Maintenance This policy should be reviewed when relevant systems, laws, platforms, organizational structure, or operational practices materially change. Credential Requirements Unique passwords. 2FA on supported administrative services. Secure recovery methods. No credential sharing in Discord/DMs/tickets. Prompt rotation after suspected exposure. Privileged Accounts Root, organization-admin, database-admin, domain/DNS, production deployment, and equivalent access should be limited to people who actually require it. Definitions & Interpretation Where a term is not specifically defined in this policy, it should be interpreted using its ordinary GGU operational meaning and related published guides. When two policies appear to conflict, the more specific policy should generally control for its subject matter unless higher Leadership directs otherwise. Policy Ownership Each policy should have an identifiable organizational owner responsible for periodic review, proposed updates, and resolving routine interpretation questions. Ownership of the policy does not grant unlimited authority to waive it. Records & Evidence Keep records that are reasonably necessary to demonstrate approvals, access changes, disciplinary actions, incidents, or exceptions. Store sensitive records in appropriately restricted locations. Do not create unnecessary collections of personal information. Do not alter or delete records to conceal mistakes or avoid review. Where an action is logged automatically, preserve the relevant log rather than duplicating it manually without need. Good-Faith Reporting Members and Leaders should be able to report suspected policy violations in good faith without retaliation. Knowingly false reports, fabricated evidence, or malicious misuse of reporting processes may themselves be addressed as misconduct. Policy Changes Material policy changes should be communicated to affected people. Changes that alter access, enforcement, or Leadership obligations should include enough explanation for people to understand what changed and when the new expectation applies. Access Lifecycle Request Approval Provisioning Verification Periodic review Modification after role change Removal/offboarding Recovery Codes Recovery codes and emergency credentials should be stored securely and not pasted into normal chat channels. Where GGU maintains organizational recovery access, ownership should not depend on one individual's personal device. Policy protects the community when expectations are clear before problems happen.
-
Leadership Code of Conduct & Ethics Policy Organization-Wide Leadership Standards This guide may be updated as GGU policies, procedures, platforms, and organizational needs change. Public Transparency: This policy is intentionally published for community transparency. The policy itself is public; credentials, recovery material, private personnel records, security-sensitive evidence, and other protected operational details remain restricted. Purpose GGU Leadership — including Moderator, Staff, Manager, Senior Manager, Operations Leader, Community Leader, and the Owner when acting in a Leadership capacity — is entrusted with authority, access, and community influence. This policy establishes minimum conduct standards for anyone holding Moderator or higher Leadership responsibilities. Required Conduct Act in good faith for GGU and its community. Treat people respectfully. Use authority consistently and proportionately. Protect confidential information. Disclose conflicts of interest. Accept reasonable accountability for administrative actions. Prohibited Conduct Retaliation against reporters or critics. Favoritism in enforcement or personnel decisions. Using administrative tools for personal disputes. Harassment or humiliation of members or Staff. Falsifying records or evidence. Accessing private information without a legitimate operational reason. Enforcement Violations may result in coaching, warning, access restriction, suspension, demotion, or removal depending on severity. Scope This policy applies to GGU members, Leadership, contributors, partners, or systems to the extent they participate in or affect the activity described by this policy. Responsibilities Individuals are responsible for complying with the policy within their assigned access and duties. Managers are responsible for communicating expectations and correcting known violations within their area. Higher Leadership may interpret organization-wide questions, approve exceptions, or impose additional controls where risk requires it. Exceptions Exceptions should be limited, justified by a legitimate operational need, approved by the appropriate authority, and documented when they materially increase risk or depart from normal practice. Violations Violations may result in corrective instruction, removal of access, warning, suspension, demotion, removal from Leadership, removal from the community, or other action appropriate to the severity and circumstances. Review & Maintenance This policy should be reviewed when relevant systems, laws, platforms, organizational structure, or operational practices materially change. Abuse of Authority Threatening punishment to settle personal disagreements. Using private information for embarrassment or leverage. Selective rule enforcement based on friendship or dislike. Retaliating against good-faith complaints. Using privileged access for curiosity rather than a legitimate GGU purpose. Impairment Do not perform sensitive administrative, moderation, disciplinary, or production actions while significantly impaired. Definitions & Interpretation Where a term is not specifically defined in this policy, it should be interpreted using its ordinary GGU operational meaning and related published guides. When two policies appear to conflict, the more specific policy should generally control for its subject matter unless higher Leadership directs otherwise. Policy Ownership Each policy should have an identifiable organizational owner responsible for periodic review, proposed updates, and resolving routine interpretation questions. Ownership of the policy does not grant unlimited authority to waive it. Records & Evidence Keep records that are reasonably necessary to demonstrate approvals, access changes, disciplinary actions, incidents, or exceptions. Store sensitive records in appropriately restricted locations. Do not create unnecessary collections of personal information. Do not alter or delete records to conceal mistakes or avoid review. Where an action is logged automatically, preserve the relevant log rather than duplicating it manually without need. Good-Faith Reporting Members and Leaders should be able to report suspected policy violations in good faith without retaliation. Knowingly false reports, fabricated evidence, or malicious misuse of reporting processes may themselves be addressed as misconduct. Policy Changes Material policy changes should be communicated to affected people. Changes that alter access, enforcement, or Leadership obligations should include enough explanation for people to understand what changed and when the new expectation applies. Professional Boundaries Leaders may be friends with community members and other Staff. Personal relationships are normal, but Leadership actions must still be based on policy and evidence. Leaders should avoid using private access to monitor, embarrass, or gain leverage over people outside legitimate GGU needs. Public Conduct Leadership members are not expected to be formal at all times, but public conduct should not reasonably undermine trust in moderation, security, or organizational decision-making. GGU Leadership Hierarchy The general organization-wide Leadership hierarchy is: Community Leader — highest community leadership layer and organization-wide oversight. Operations Leader — day-to-day organization-wide operations and direct oversight of Senior Managers. Senior Manager — oversees Managers and broader operational areas. Manager — directly manages an individual Team or Department. Staff — game-server Leadership supporting Managers and Moderators. Moderator — routine game-server moderation and enforcement. Escalation: For organization-wide escalation, the normal path is Moderator → Staff → Manager → Senior Manager → Operations Leader → Community Leader. Not every issue must pass through every level. Current Leadership Assignments Current role holders are maintained on the GGU Ranks & Roster page. This policy governs the role regardless of who currently holds it. Policy protects the community when expectations are clear before problems happen.
-
Resource Directory Community, Documentation & Service Links This guide may be updated as GGU policies, procedures, platforms, and organizational needs change. This directory provides a single place to find the primary public GGU resources. Use live directories and current forum categories instead of maintaining duplicated static server lists. Community Main Website: https://gguclan.com/ Forums: https://gguclan.com/forums/ Discord: https://discord.gg/ggu Server Directory: https://gguclan.com/servers/ Documentation Community Resources: Use the Community Resources forum for general guides and references. Guides: Use the Guides forum for Leadership and technical procedures. Policies Center: Use the Policies Center for organization-wide policy. Rule Enforcement Procedures: Use the enforcement forum for global and game-specific moderation procedures. Keeping This Directory Current Prefer stable GGU URLs over direct links to temporary infrastructure. Do not duplicate server IP lists when the live server directory already exists. Retire broken or superseded links promptly. If a resource moves, update this directory and any high-traffic onboarding guides. Resource Ownership Each major resource should have a clear owner responsible for keeping links, descriptions, and access information current. When a Resource Moves Update the canonical Resource Directory. Update onboarding guides and high-traffic references. Leave redirects where practical. Retire duplicate or obsolete links. Verify old bookmarks or automation do not depend on the previous URL. Questions & Edge Cases I am missing a role: contact Leadership and provide the platform/account affected. I changed my username: update your profile/account information where possible so Leadership can still match your identities. I left for a long time: returning does not necessarily require a new application; contact Leadership if status is unclear. I joined through one game: you may still participate across the rest of GGU. I disagree with a moderation decision: use the appropriate review or appeal process rather than escalating the dispute publicly. Documentation Principle Community-facing guides should point to current canonical resources instead of copying volatile information such as live server IPs, temporary invite links, or changing staff rosters. This reduces broken information and keeps updates manageable. One directory. Current links. Less documentation drift.
-
Public Documentation & Transparency Standard What GGU Publishes and What Must Remain Protected Documentation standard for Community Resources and related public forums. GGU's Community Resources, Guides, Policies Center, and Rule Enforcement Procedures are intended to be useful to both Leadership and the wider community. Transparency is the default for standards, expectations, authority, and procedures. What Should Be Public Leadership structure and responsibilities. Leadership conduct and ethics standards. Promotion, demotion, discipline, and recusal standards. Administrative access expectations such as least privilege and 2FA. Control Center and repository usage policies. Moderation authority and enforcement procedures. Appeal and abuse-report processes. Member activity and Leave of Absence standards. Technical guides that do not expose secrets. General incident-response expectations and accountability. What Should Remain Restricted Passwords, tokens, private keys, recovery codes, and secret values. Private personnel records and detailed disciplinary evidence. Non-public abuse-report evidence containing personal or sensitive information. Unreleased vulnerability details that could enable abuse. Security architecture details that materially increase attack risk. Private member data not needed for public accountability. Incident data whose disclosure would interfere with an active investigation or recovery. Public Does Not Mean Uncontrolled A public guide may describe that a system uses privileged roles, approval workflows, evidence standards, or access reviews without publishing the credentials or confidential records used to operate those systems. Writing Standard Explain what GGU expects and why. Use plain language where possible. Define authority and escalation clearly. Avoid vague threats or unnecessary legal claims. Do not publish temporary credentials, internal-only identifiers, or live secret values. Use canonical links instead of copying volatile information. State when a procedure contains discretion rather than pretending every situation is identical. Transparency & Accountability Publishing Leadership policies allows members to understand the standards GGU applies to its own Leaders. Members should be able to know what conduct is expected, how conflicts are handled, how abuse can be reported, and how administrative authority is supposed to be used. Transparent standards. Protected secrets.
-
Magic Weaving: A Beginner's Guide The Basics What Is It What Is Magic Weaving? Magic Weaving is Wizard101's system for picking a second "Weaving School" alongside your main school, then ranking it up over time. As you rank up, you unlock cross-school spells, jewels, pets, and Fusion Formulae tied to whichever combination you chose — letting a Fire wizard borrow Ice's defensive tricks, a Life wizard pick up Storm's burst damage, and so on. Key terms: › Weaving School — the second school you choose to develop, separate from your wizard's main school › Blended Grove — the hub area in Selenopolis where each school has its own magic tree › Magic Weaving Tome — tracks your lesson progress for whichever school's tree you're weaving with › Fusion Formulae — some rank rewards combine effects from your main school and your Weaving School into one new spell Getting Started Unlocking Magic Weaving 1. Finish the Dragonspyre main storyline — this is what triggers the new questline into Selenopolis 2. Play through the Selenopolis intro quests, which also cover Archmastery and Magic Wheel tutorials, until you're guided to the Blended Grove 3. In the Blended Grove, talk to the tree matching the school you want to weave into — this locks in your Weaving School 4. Work through that tree's Magic Weaving Lessons to earn your first rank of rewards Choose your Weaving School deliberately. There's no confirmed easy reset, so pick a combination that actually covers a gap in your main school's kit rather than whatever looks fun on the character select screen. Ranking Up Magic Weaving is organized into ranks, and KingsIsle has added new ranks through content updates rather than all at once. Each rank layers new lessons onto your chosen tree, and rewards vary by school — some schools get new Fusion Formulae, others get utility spells, and others get a new pet and jewels. Ranks 1–3 The original Selenopolis foundation Open to anyone past Dragonspyre Rank 4 Requires Rank 3 plus the Avalon storyline finished Balance/Ice get new Fusion Formulae; Storm/Life get utility spells; Fire/Myth/Death get a pet and jewels Rank 5 Newest rank, Karamelle-themed Tip: Open your chosen tree and select "Magic Weaving Tome" to see badge progress for that school's lessons — no more digging through your quest log to check where you left off. Tips & Common Mistakes Picking a school at random — without checking what your main school lacks (defense, healing, utility), you can grind out a whole rank for rewards you'll never actually use Ignoring your main storyline — Rank 4 gates behind finishing Avalon, so skipping ahead in story worlds can quietly block your Weaving progress later Confirm you've finished Dragonspyre before expecting Selenopolis quests to appear Talk to the correct tree in the Blended Grove for the school you actually want Keep pushing your main storyline alongside your lessons, since later ranks gate on story progress FAQ Do I need to finish the whole game before I can start? No — you can start Magic Weaving right after Dragonspyre. Later ranks, like Rank 4, do require finishing further story worlds such as Avalon. Does every wizard on my account need the same Weaving School? No, the choice is per wizard, so each of your alts can develop a different Weaving School combination. Just Starting Ranks 1–3 Finish Dragonspyre, pick your tree, and start your first lessons Late Game Rank 4+ Keep pace with your main storyline to unlock each new rank as it drops Questions about Weaving? Ask in the Wizard101 channels or reach out to Guild Staff.
-
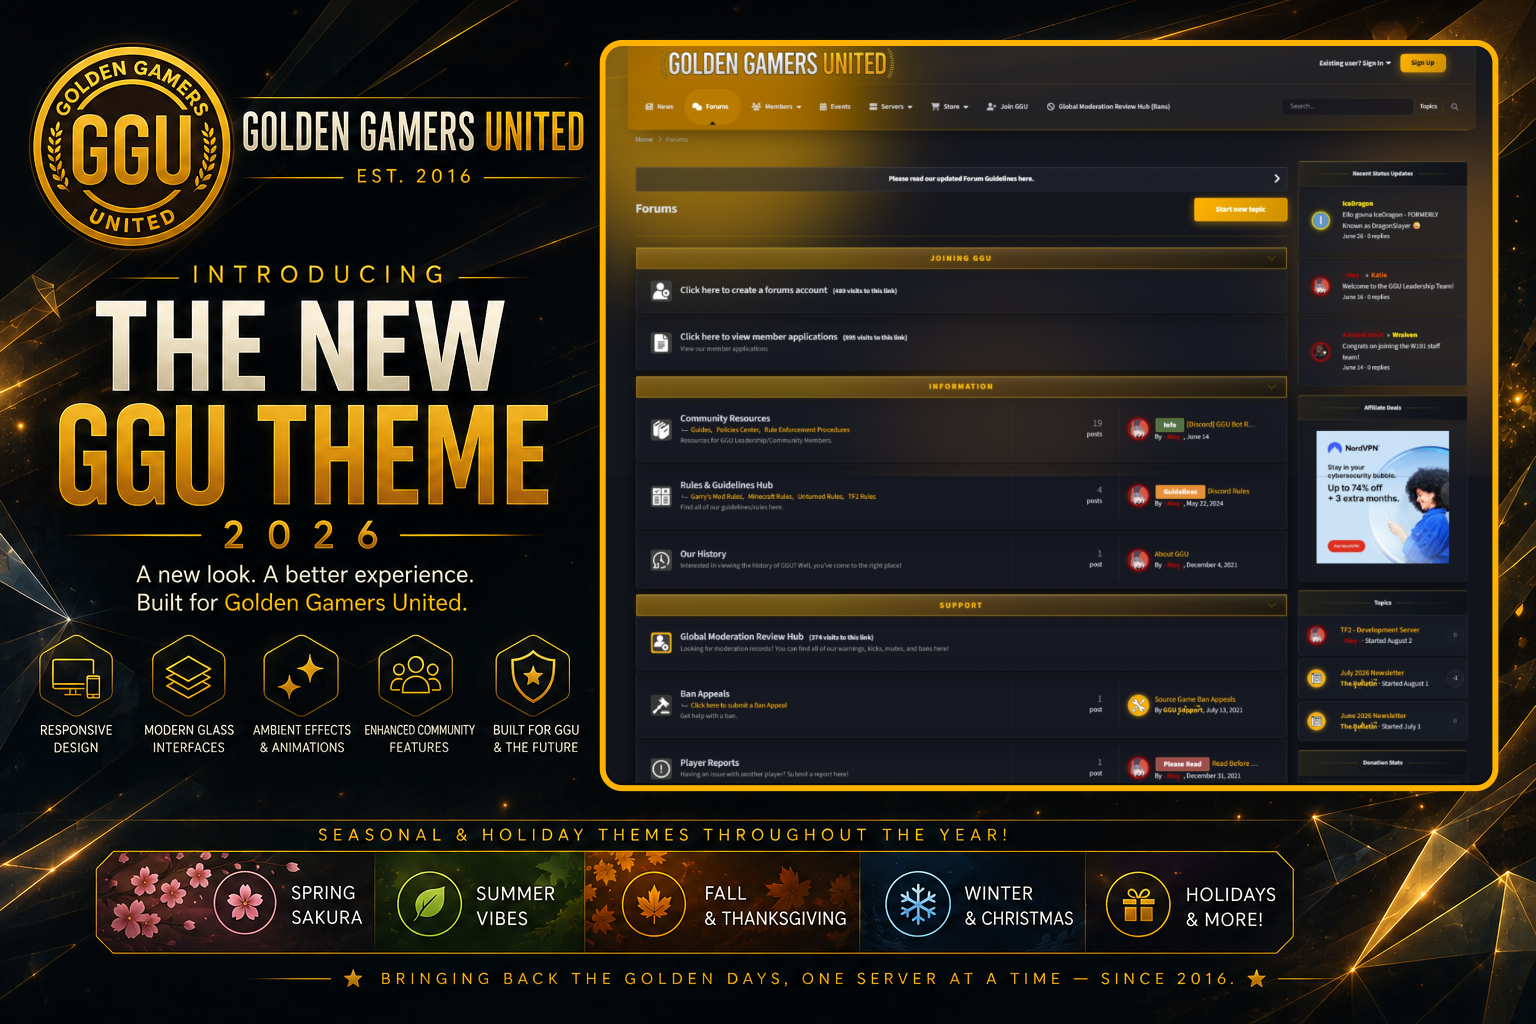 Introducing the New GGU Theme for 2026 A new look. A new experience. The same Golden Gamers United. Welcome to the New GGU We're excited to officially introduce the new Golden Gamers United Theme for 2026! Over the past several weeks, we've been working on a significant redesign of the GGU web experience. This wasn't simply about changing a few colors or updating some buttons. We wanted to create a visual identity that feels distinctly GGU while modernizing the experience across the entire community. The result is a new dark gold, amber, and bronze design built around glass interfaces, ambient lighting, prism-inspired effects, subtle animations, and a much more unified presentation across the site. What's New? A New Visual Identity A completely refreshed dark glass design featuring GGU's new gold, amber, and bronze visual language. Ambient Effects New lighting, prism effects, backgrounds, animations, and environmental details throughout the community. Responsive Design Improved layouts and navigation across desktop, tablet, and mobile devices. Community Integration Enhanced styling for member groups, ranks, profiles, widgets, forums, menus, and community features. Seasonal & Holiday Themes One of the biggest additions to the new theme is something you'll see evolve throughout the year: GGU can now change with the seasons. We're developing seasonal variants that can temporarily transform the community with different colors, backgrounds, decorations, and environmental effects. Winter & Christmas Snowfall, winter atmosphere, festive accents, and holiday styling. Halloween Spooky colors, atmospheric effects, and Halloween decorations. Spring Brighter seasonal accents accompanied by falling Sakura/cherry blossom effects. Fall & Thanksgiving Warm autumn colors and seasonal environmental effects. U.S. Holidays Special variants for major holidays throughout the U.S. calendar. Keep an eye on the site! Some themes may appear for an entire season, while others may only be activated for a particular holiday or weekend. You never know exactly what GGU might look like the next time you visit. Built for Golden Gamers United This isn't an off-the-shelf theme with a GGU logo placed on top. The new theme has been developed specifically for Golden Gamers United and is designed to continue growing alongside the community. That means today's release isn't the end of development. We'll continue refining the design, improving mobile support, fixing edge cases, developing seasonal variants, and expanding the new visual language into other areas of GGU. Found Something We Missed? The theme is still actively being improved. With a redesign this extensive, there may still be a few things hiding in the corners. If you encounter a visual bug, broken menu, mobile layout issue, or something that simply doesn't look right, please report it so the Development Team can investigate. Feedback is also welcome. Many improvements made during development came directly from seeing how the theme behaved during real-world use. Welcome to the New GGU Golden Gamers United has changed quite a bit since 2016, but our goal remains the same: build a community where people can find great servers, great games, and people worth playing them with. This redesign is another step toward giving that community a home that reflects what GGU has become. Thank you to everyone who has supported, tested, and provided feedback throughout development. Welcome to the new Golden Gamers United. — The GGU Development Team Bringing back the golden days, one server at a time — since 2016.
-
Development Server This server is a testing ground for content that isn't ready for prime time. Looking for our stable servers? Click here to view our server list! ⚠ Heads up before you join This is an active development environment, not a finished product. Maps, plugins, and configs here are being built and tested in real time, which means things can and will break. › Expect instability — crashes, bugs, and broken features are normal here, not the exception. › Content changes without notice — maps, settings, and plugins may be swapped, reset, or removed at any time. › No stat/progress guarantees — stats, unlocks, or saved data on this server may be wiped during testing. › Feedback welcome — found a bug or have a suggestion? Let us know in Discord so we can squash it.
-
Event Coordinator Guide Overview This guide covers the four event categories GGU runs for Wizard101, how each one is set up, and how to adapt on the fly depending on turnout. Read through the whole thing before coordinating your first event. The Four Event Categories: › Guild Benefit Events — anything that benefits the guild (Guild Museum, Guild Meeting) › Player Benefit Events — anything that benefits players (Boss Farming, Questing, Cantrip Chest Farming, Beastmoon, Decathlon, Portal of Peril, Challenge Mode, Gear Farming, etc.) › PvP Events — anything having to do with PvP (Tournaments, Practice PvP, etc.) › Raid Events — anything having to do with raids Guild Benefit Events Guild Museum Setup Guild Museum events run on what the museum currently needs — not a fixed routine. Before grouping anyone up, check the museum itself. › Go into the Guild Museum and check which exhibits need Prima Materia › Identify what's required to get that Prima Materia for the needed exhibits › Divide attendees into groups based on turnout (e.g. 7 players → 4+3, 8 players → 4+4, etc.) › What groups actually do — Bosses, Minions, or Cantrip Farming — depends on headcount and what the museum needs Guild Meeting Setup Guild Meetings are whole-guild gatherings — no grouping required. The purpose is to review where the guild currently stands and what needs to be worked on going forward. Player Benefit Events Cantrip Chest Farming (Spellements) Setup This is one of our most common Player Benefit events — everyone needs spellements, so it runs often. › Divide attendees into groups of 3 › If attendance does not divide evenly into 3s, pivot — randomly pick a player, find out what they personally need, and have the group go help them with that instead Beastmoon, Decathlon, Portal of Peril & Challenge Mode Setup These events follow the same layout as Guild Museum Events — divide attendees into groups based on turnout (4+3, 4+4, etc.) and assign each group accordingly. PvP Events Setup PvP — Tournaments, Practice PvP, etc. — is not currently a primary focus for GGU. › Coordinators have flexibility here — design whatever format, group sizes, and structure work best for the event. No fixed template exists yet. Raid Events Current Status Raids haven't launched for GGU yet, so this setup is still in early planning. What we know so far: › Minimum of 12 players › Minimum character level of 160 › Advanced combat rules apply — this is part of why spellements matter This section will be updated once group composition, role rules, and farming requirements are finalized. Coordinator Notes Cantrip Chest Farming shows up in two places — is that a miscategorization? No — it's correctly dual-purpose. It's a tool used inside Guild Museum events (Guild Benefit) when an exhibit needs Prima Materia, and it's also its own standalone Player Benefit event for spellements. Just be clear going in on which "version" you're running, since the goal changes which targets the group should prioritize. Is everything else categorized correctly? Yes. Guild Museum and Guild Meeting sit correctly under Guild Benefit since they serve the guild collectively, and Boss Farming, Questing, Beastmoon, Decathlon, Portal of Peril, Challenge Mode, and Gear Farming all sit correctly under Player Benefit since the payoff goes to the individual player. Summary — Setup Quick Reference › Guild Museum — check exhibit needs first, then group by turnout (4+3, 4+4, etc.) › Guild Meeting — whole-guild, no grouping needed › Cantrip Chest Farming — groups of 3, pivot to helping one player 1:1 if it doesn't divide evenly › Beastmoon / Decathlon / Portal of Peril / Challenge Mode — same group-by-turnout layout as Guild Museum › PvP — coordinator's discretion, no fixed format yet › Raids — 12 players minimum, level 160+, advanced combat rules (planning stage) Questions about event setup? Reach out to Wizard101 Leadership.
-
GGU Bot Role Assignment Commands Commands are used to assign roles via GGU Bot. Always run the mainline role command first before the game-specific tag. If you need Server Manager or Community Manager access on any platform (including Discord) please ping @ Alex Thunderhunter or @ Admiral MacK for help. All commands are toggles — you can add or revoke roles with the same command. If you have access to give a role, you have access to revoke it. When promoting anyone to a higher rank, fully remove their previous access before granting their new access to prevent the spacer roles from breaking. Example: Promoting someone to TF2 Moderator: !mod @user — Assigns the global Mod role !tf2mod @user — Assigns the TF2 Mod tag role Global Roles Core hierarchy roles. Run these first when assigning any staff position. › !member — Member › !staff — Staff › !mod — Mod › !manager — Manager › !seniormanager — Senior Manager › !retired — Retired Specialized Roles Standalone roles for specific departments. No paired mainline command needed. › !dev — Developer › !outr — Outreach › !des — Design › !devmanager — Dev Manager › !unimanager — Universal Manager Game-Specific Tags All game-specific commands assign only the game tag. Pair with a global role command (e.g. !staff, !mod, !manager). Team Fortress 2 › !tf2staff — TF2 Staff › !tf2mod — TF2 Mod › !tf2manager — TF2 Manager Minecraft › !mcstaff — MC Staff › !mcmod — MC Mod › !mcmanager — MC Manager Wizard101 › !w101staff — W101 Staff › !w101manager — W101 Manager BeamMP › !bmpstaff — BMP Staff › !bmpmod — BMP Mod › !bmpmanager — BMP Manager Unturned › !untstaff — UNT Staff › !untmod — UNT Mod › !untmanager — UNT Manager Garry's Mod › !gmodstaff — GMod Staff › !gmodmod — GMod Mod › !gmodmanager — GMod Manager CS:GO › !csgostaff — CSGO Staff › !csgomod — CSGO Mod › !csgomanager — CSGO Manager Rust › !ruststaff — Rust Staff › !rustmod — Rust Mod › !rustmanager — Rust Manager Hytale › !hytstaff — Hyt Staff › !hytmod — Hyt Mod › !hytmanager — Hyt Manager Arma Conflict › !acstaff — AC Staff › !acmod — AC Mod › !acmanager — AC Manager
-
Approved Katie SolarBlood's Member Application
- Alex - replied to Katie's topic in Processed Member Applications
Approved - Welcome to Golden Gamers United

